
Elastic Cloud Billing data collection and Kibana dashboard
Pulls Elastic Cloud Billing information from the Billing API then sends it to an Elasticsearch cluster and visualizes the results in Kibana dashboards.

Get content for Kibana, Elasticsearch, Logstash and more
Elastic Content Share
Download overview
Elastic Observability dashboards help SREs, DevOps engineers, and platform teams understand service health with logs, metrics, traces, uptime checks, APM data, Kubernetes signals, OpenTelemetry data, and SLO context.
Use this category when you need a faster start for operational monitoring, incident review, or service dashboards. Many examples expect data from Elastic Agent, Beats, APM agents, Metricbeat, Filebeat, Kubernetes integrations, or OpenTelemetry collectors. Check the expected data source before importing.
Prebuilt dashboards save time because they show useful field groupings, filters, and visual patterns. They also help teams learn how logs, metrics, and traces can support root-cause analysis in Kibana.
Related resources include Kubernetes Observability, AI root-cause workflows, Logstash pipelines, and the official Elastic Observability overview.
Observability examples work best when the data source is clear. Check whether the download expects Elastic Agent integrations, Beats modules, APM agents, Kubernetes metadata, or OpenTelemetry fields. If your environment uses different service names or labels, adapt the filters first. Then use the dashboard during a test incident or game day before relying on it in production.
Use these downloads together with service ownership and deployment context. Observability content is strongest when a dashboard helps a responder answer what changed, who is affected, and what signal should be checked next.
Use this collection
Elastic Observability examples help observability teams analyze logs, metrics, traces, uptime, and operational signals with reusable Elastic dashboards and content.
Download the content, import it into your Elastic environment, review the saved objects or rules, and adapt the fields, filters, and visualizations to your own data.
Use the related collections below to move between dashboards, security content, observability examples, pipelines, Elasticsearch resources, and AI-assisted Elastic workflows.
Pulls Elastic Cloud Billing information from the Billing API then sends it to an Elasticsearch cluster and visualizes the results in Kibana dashboards.
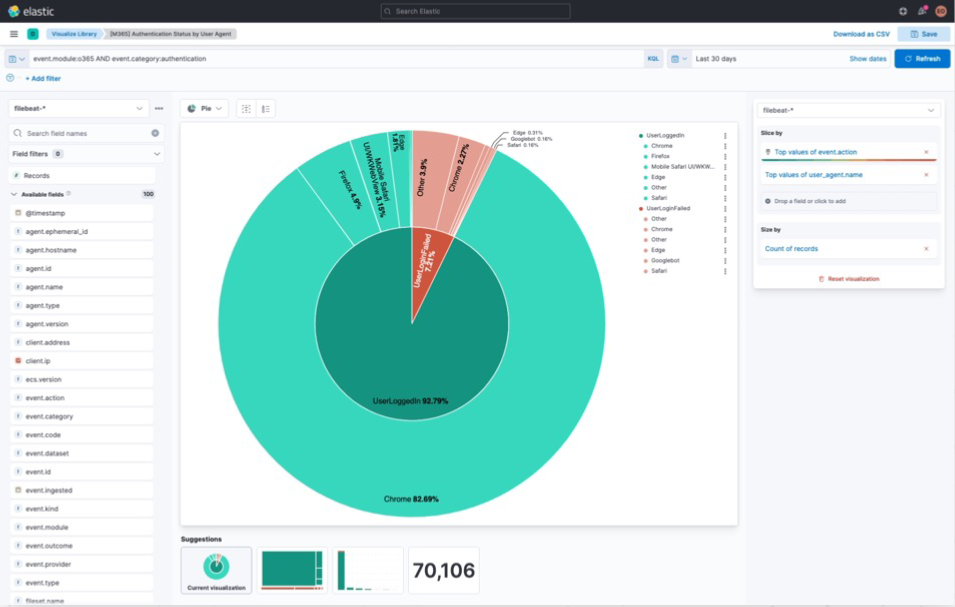
A collection of Kibana dashboards to provide a holistic view of Microsoft Office 365 environments
Cloudflare dashboards and ingest pipelines to visualize cloudflare logs

This is a simple canvas dashboard example that analyzes logs created by Filebeat.
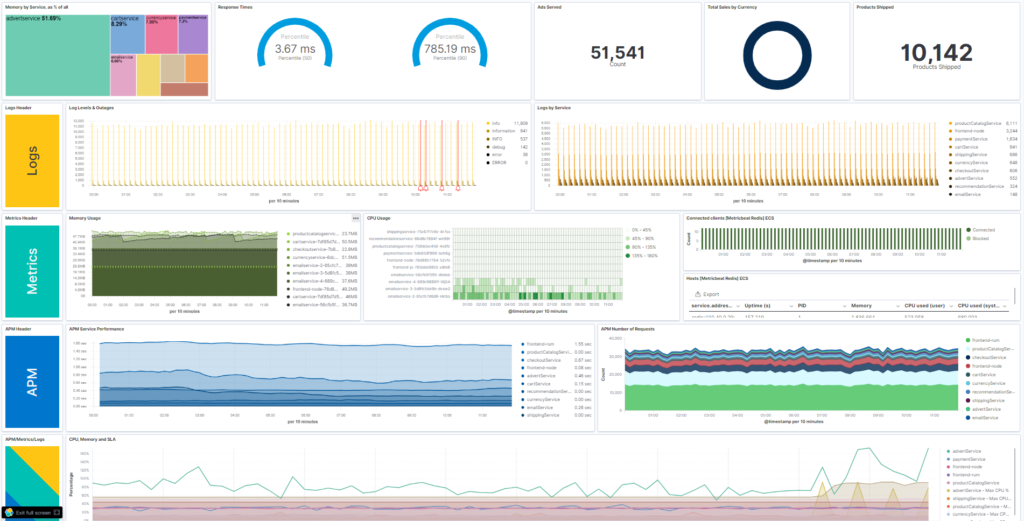
A single pane of glass dashboard for Logs, Metrics, APM data and business KPIs.

An adaptive turn key canvas example based on Elastic APM data.
This watch is getting data from the Elasticsearch shards API directly and checking for large shards.
A watch which alerts if the time spent by a hosts CPU in IOWait, has increased by more than than N% in the last Y mins.

This dashboard provide deeper insight into the real user monitoring data collected by Elastic RUM.